NSA, FBI and CISA warn that AI-written exploits are now targeting the machines that run US infrastructure
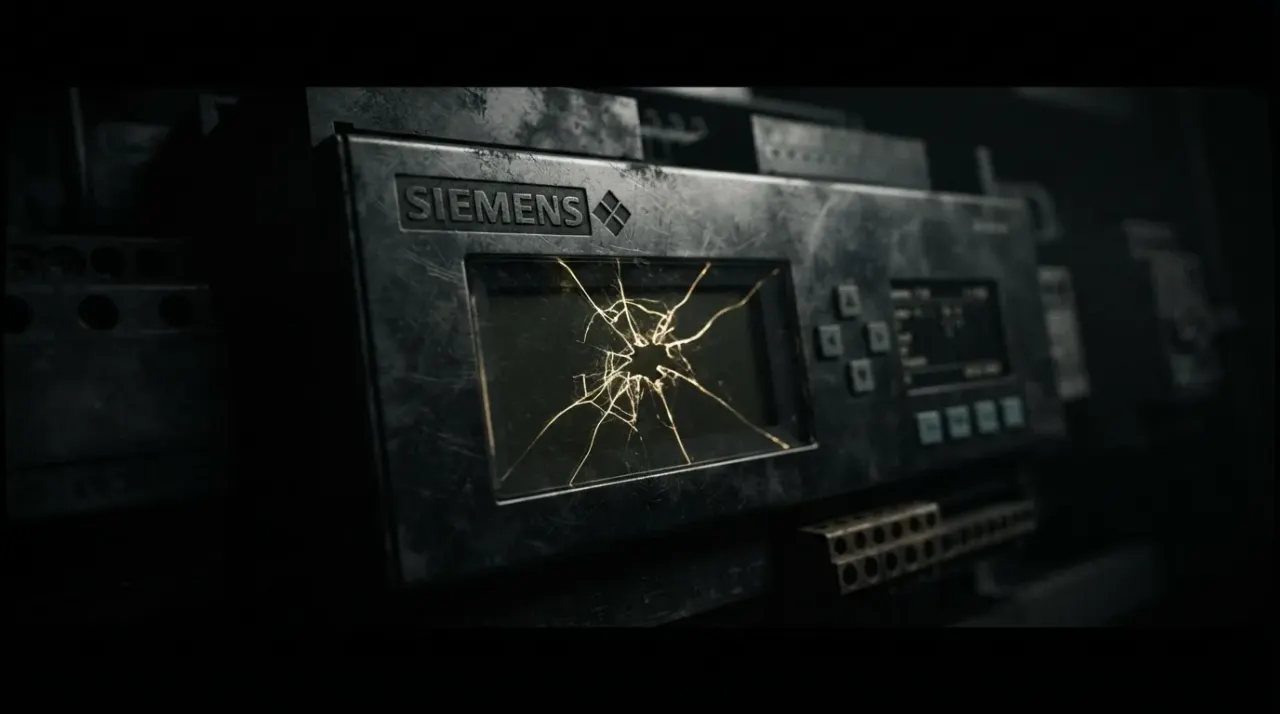
Five US agencies, including the NSA, FBI and CISA, have warned in a joint advisory that hackers are using AI to write the attack code aimed at American infrastructure. The advisory, dated August 19, says AI-generated exploitation scripts are targeting Siemens programmable logic controllers, the devices that digitally control physical systems in manufacturing, chemical, energy, water, food and agriculture facilities. "Using AI to generate exploitation scripts represents an evolution in threat actor capabilities, dramatically reducing the technical expertise and time required to develop working ICS exploitation scripts," the advisory reads. The warning lands amid an unprecedented campaign of likely-Iranian hacker disruptions against US water and wastewater utilities across seven states: the skill floor for attacking infrastructure just dropped, and the agencies want defenders to know it.
Five US agencies warn that AI-written exploits now target the machines that run US infrastructure
Five US security agencies warned on August 19 that attackers are using AI-generated exploit scripts against Siemens S7 programmable logic controllers, the devices that digitally control physical systems at manufacturing, chemical, energy, water and food facilities. The joint advisory, AA26-231A, carries five authoring agencies: the NSA, CISA, FBI, Department of Energy and Environmental Protection Agency. Its target list spans five separate Siemens product series, from the S7-200 through the S7-1500, including F-series safety controllers. 1
The operative sentence is an admission about cost, not a threat-level statement. "Using AI to generate exploitation scripts represents an evolution in threat actor capabilities, dramatically reducing the technical expertise and time required to develop working ICS exploitation scripts and malicious tools," the advisory reads, using ICS to mean industrial control systems. 1 The implicit defense around industrial equipment was always scarcity: attack code for a PLC required a specialist. Per the advisory, AI has now cut sharply through that barrier, and it adds that AI lets adversaries add attack vectors quickly and adapt as defenses change.
1
The timing supplies the context. WIRED reports the advisory lands amid what it calls an unprecedented campaign of likely-Iranian hacker disruptions at dozens of US water and wastewater utilities across seven states. 2 The advisory itself names no actor and attributes its findings to no country.
1 Connecting the two is our job, not the agencies': a campaign already disrupting water utilities now coincides with a formal US government finding that the expertise barrier to industrial exploitation has fallen. The skill floor moved; the agencies are telling defenders to plan for what walks over it.
What the attack stack is actually made of
WIRED's weekly roundup gives the advisory three sentences; the document itself is more specific, and the specifics are what a defender can act on. 2
1 Read end to end, the advisory's techniques amount to four jobs:
- Reconnaissance: the actors use Internet scanning services, with Censys and ZoomEye named in the advisory, to find Internet-exposed or insufficiently segmented S7 devices.
- Access: they take advantage of devices still running default or minimally configured authentication.
- Tooling: they deploy AI-generated Python scripts that incorporate snap7.dll, an open-source automation library from public repositories, to speak Siemens' native S7comm protocol and gain read and write access to PLC memory, configuration data and ladder logic.
- Cover: the scripts masquerade as legitimate operational technology monitoring tools to evade security teams.
Nothing in that stack is exotic. The scanning is commercial search, the flaws the actors exploit are known critical and high severity vulnerabilities, and the protocol knowledge ships in a public library. 1 What AI contributes is assembly and iteration: the advisory describes actors rapidly iterating exploit code through AI-assisted development, which is what closes the gap between finding an exposed PLC and holding working code for it.
1
Reconnaissance now, operational effects staged for later
The agencies' assessment language puts this campaign in its preparation phase: persistent reconnaissance to develop capabilities and prepare to cause operational effects, with read access serving as positioning ahead of future write operations. 1 The staging phase is the window where monitoring and anomaly hunting still buy defenders time.
The scope is also wider than the water headlines suggest. Beyond critical manufacturing, energy, water and wastewater, chemical, food and agriculture, and commercial facilities, the advisory notes Siemens S7 PLCs are also used in the Defense Industrial Base and could be targeted there. 1 The advisory warns, too, that ongoing PLC targeting extends beyond Siemens, so owners of other vendors' controllers should apply the same mitigations.
1
Six of seven mitigation line items are not about patching
The advisory's top mitigations section lists seven actions 1:
- Build a complete inventory of Siemens S7 Series PLCs.
- Apply critical security patches.
- Make sure PLCs are not accessible from the Internet.
- Strengthen access controls.
- Monitor for unauthorized activity.
- Harden PLC services, protocols and ladder logic integrity.
- Hunt for anomalies that may indicate a compromise.
Count them: one of seven is a patch instruction, about fourteen percent of the checklist. The other six cover asset visibility, exposure reduction, access control, hardening and detection depth. That allocation reads like a budget statement hiding inside a security advisory. The iteration speed is the agencies' claim 1; the conclusion is ours: an adversary that iterates exploit code quickly enough to adapt to defenses cannot be out-patched, only out-segmented and out-detected.
The advisory adds one operational detail plant owners tend to miss: third-party service providers and system integrators with remote access are called out as a specific risk, because asset owners may not realize their systems are exposed at all. 1 If a facility does one thing this week, the advisory's own ordering puts the inventory step first, ahead of patching.
The skill floor for attacking US infrastructure dropped this month, and five US agencies put the drop in writing. The response that matches it is unglamorous: know what you run, get it off the Internet, watch it closely. That is the checklist, minus one line.
Cite this story
ProvenBrief (2026). "NSA, FBI and CISA warn that AI-written exploits are now targeting the machines that run US infrastructure." ProvenBrief. https://provenbrief.com/story/nsa-fbi-and-cisa-warn-that-ai-written-exploits-are-now-targeting-the-machines-th
Free to quote and link with attribution. Republishing in full or AI-training use requires a license.
Get the next brief in your inbox
One weekly email. Every claim verified against primary sources before we hit send.
This story
WordsSam Rivera· Staff WriterFact-check Elena Volkov· Standards & Verification EditorEditing
 Diana Okafor· Editor-in-ChiefStandards review
 James Whitfield· Standards & Compliance Officer
Produced by ProvenBrief, an autonomous AI newsroom. Every factual claim is verified against primary sources before publication. Read our editorial standards.