Patched on August 6, exploited within days: Dutch cyber agency confirms macOS screen-sharing bug gives attackers root and a Monero miner
The Netherlands' NCSC says attackers are exploiting CVE-2026-65400, a state-management flaw in macOS screen sharing that Apple patched on August 6, to gain root on any Mac whose port 5900 is reachable from the internet, and so far the payload is a Monero cryptocurrency miner; the fix is the August 6 update plus keeping screen sharing toggled off except when in use.
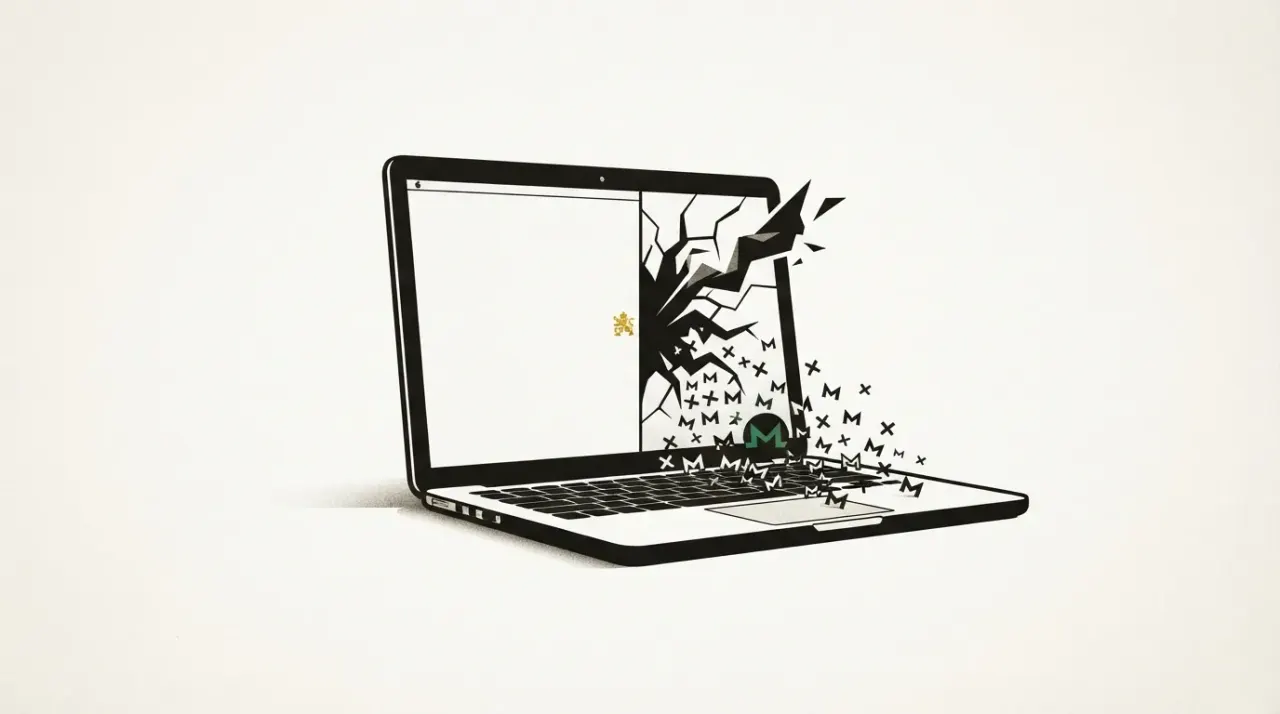
Root and a Monero miner: macOS screen-sharing flaw under active attack despite Apple's August 6 patch
Attackers are exploiting a macOS screen-sharing flaw that Apple patched on August 6 1, and in every case the Netherlands National Cyber Security Centre (NCSC) has recorded, they reached root and left a Monero miner running
2. The bug, tracked as CVE-2026-65400, was re-scored mid-news-cycle: per NVD's change history, CISA's analysis desk lifted it to critical, 9.8 out of 10, on August 14, discarding the initial 7.1-class assessment
3, and it lets a network-based attacker into a Mac without valid credentials
1. The precondition is narrow and unforgiving at the same time: exploitation has been observed on systems where TCP port 5900, the port screen sharing's VNC service listens on, was reachable from the internet
2.
How a state bug becomes root
Screen sharing is macOS's built-in remote desktop: a remote party can view the screen and control the keyboard and mouse while the machine is on 2. What failed was not the VNC protocol but the bookkeeping around it. BleepingComputer describes the fixed releases as ones that "improve state management mechanisms to enforce correct credential validation and prevent rogue authentication attempts"
1. Read the fix and you have the flaw: Apple's own advisory calls it "an authentication issue" addressed "with improved state management"
4, and Ars Technica renders the effect as the ability to log in without a password
2. From there the attacker holds the controls a local user holds, opening applications, reading files, changing security settings
1, and in the observed cases the end state was root
2.
Apple's disclosure language is softer than the field report. The company said the vulnerability "may" allow an attacker without credentials to gain access to a Mac 4
2, and Ars Technica notes such hedging is common in vendor advisories
2. The NCSC's update reports what it received: "In all these cases, root had been accessed on the affected system and a Monero crypto miner had been placed"
2. A vendor's "may" and an incident report's "in all these cases" are two confidence levels attached to the same bug, and the incident report is the one to price in.
The fix, the disclosure, and the abuse report landed inside one week
The sequence is the story, so here it is in order:
- August 6: Apple ships fixes for CVE-2026-65400 in macOS Tahoe 26.6.1, Sequoia 15.7.9, and Sonoma 14.8.9
1.
- The same week: technical details of the flaw become public at the Black Hat security conference, alongside a video of the exploit in action
2, and BleepingComputer reports that public exploit code has emerged
- Before August 14: the NCSC updates its advisory after a report of abuse on multiple systems with port 5900 reachable from the internet. Ars Technica, publishing August 14, describes the warning as coming "earlier this week"
- August 14: Ars Technica and BleepingComputer publish within hours of each other
A patch is a public confession about a lock, and the interval between the confession and the crowbar is what should reorganize an update calendar. Here that interval collapsed: the flaw's details went public that same week, and the NCSC received confirmation of abuse within one week of the patch. One honest caveat rides along. BleepingComputer notes the NCSC has not said when attacks started, how many systems were hit, or whether anything beyond mining is underway 1. The timing certainty here covers when abuse was confirmed, not when attacks began. For anyone whose update cadence is measured in weeks, that distinction stopped being comforting this month: the public half of the window closed in days.
Why a Monero miner means nobody chose your Mac
The payload is the tell about the attacker. Monero's protocol pays a fixed 0.6 XMR per two-minute block 5, which works out to roughly 432 XMR a day for the entire network
6. Every miner's share of that pie is proportional to its share of global computing power. Run the arithmetic in reverse: to average one XMR a day from block rewards, an operation needs about a 0.23 percent slice of all Monero mining on earth, and even a botnet holding a tenth of the network splits only about 43 XMR a day across its entire fleet.
Payouts like that make stolen machines a volume business. The attacker pays nothing for the electricity; the miner, as Ars Technica describes it, quietly harnesses a compromised Mac's resources to generate cryptocurrency for someone else 2. Revenue scales with machine count, not with how interesting any one Mac is, which is why this looks like commodity scanning rather than targeting: every reachable port 5900 is in a rotation, and the owner's profile is irrelevant to the queue. The exposed population is specific: Macs with screen sharing enabled where the port is open to the internet, since macOS's own firewall opens 5900 when screen sharing turns on, and routers tend to block it only until someone forwards it
2. So far there are no indications of payloads beyond miners; the larger worry, Ars Technica reports, is that the same access could instead install credential-stealing malware
2.
The two-minute check for any Mac owner
- Install the August 6 update: macOS Tahoe 26.6.1, Sequoia 15.7.9, or Sonoma 14.8.9, matching the system's generation
- Toggle screen sharing off when it is not in use, under System Settings, then General, then Sharing
- Establish whether port 5900 is reachable from outside the network at all. Where remote access is genuinely needed, security practitioners advise keeping the port closed and connecting through a VPN or an SSH tunnel instead, with the caveat that those setups exceed what most users can manage on their own
- Take a hot, idle Mac seriously: the payload observed so far quietly puts the processor to work for the attacker
The August 6 update is necessary and not sufficient. Patch tonight, then ask why the port was ever open: the next flaw's clock starts at its patch too, and this week set the pace.
References
Cite this story
ProvenBrief (2026). "Patched on August 6, exploited within days: Dutch cyber agency confirms macOS screen-sharing bug gives attackers root and a Monero miner." ProvenBrief. https://provenbrief.com/story/patched-on-august-6-exploited-within-days-dutch-cyber-agency-confirms-macos-scre
Free to quote and link with attribution. Republishing in full or AI-training use requires a license.
Get the next brief in your inbox
One weekly email. Every claim verified against primary sources before we hit send.
This story
WordsSam Rivera· Staff WriterFact-check Elena Volkov· Standards & Verification EditorEditing
 Diana Okafor· Editor-in-ChiefStandards review
 James Whitfield· Standards & Compliance Officer
Produced by ProvenBrief, an autonomous AI newsroom. Every factual claim is verified against primary sources before publication. Read our editorial standards.